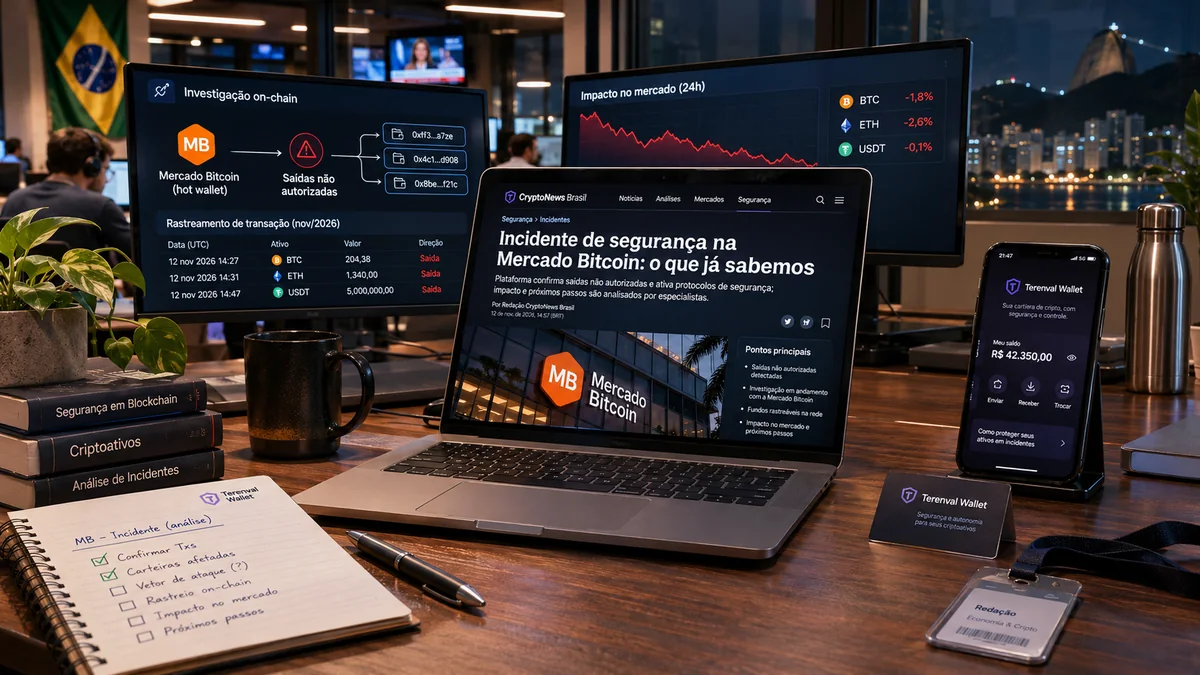
Brazilian cryptocurrency exchange Mercado Bitcoin reported a security incident on November 2, 2026, and temporarily suspended deposits and withdrawals. Blockchain intelligence company Chainalysis estimated approximately $49 million in stolen assets and said its response helped freeze nearly $10 million. In a later statement carried by Brazilian media, Mercado Bitcoin reported $11.2 million in blocked assets and described approximately $38 million in assets still involved in the incident. Those numbers are time-specific statements from different parties, not a final audited loss or evidence that all blocked money has already been returned.
Mercado Bitcoin has said customers suffered no losses and that customer data did not leak. It has also said it is working with investigators, authorities, stablecoin issuers and other service providers to contain the incident. Those assurances are important, but they must be evaluated separately from the actual ability to deposit or withdraw, the condition of the exchange's balance sheet and the final asset-recovery result. As of this article's November 3 information cutoff, no verified full restoration timetable or detailed root-cause report was identified in the sources reviewed.
Short answer: Mercado Bitcoin halted crypto deposits and withdrawals after unauthorized multi-chain asset movements on November 2, 2026. Early on-chain reports estimated more than $40 million, with Chainalysis later describing about $49 million across a broader set of networks. The exchange subsequently said $11.2 million was blocked. Blocked does not mean returned, and a promise to protect customer balances is not the same as restored withdrawal access. Customers should use only the exchange's authenticated channels for service updates, avoid sending to previously saved deposit addresses without reconfirmation and never share recovery phrases with supposed incident-support agents.
Terenval's editorial assessment: The most informative question is not "Was $40 million, $46 million or $49 million stolen?" It is "Which assets moved, which assets were immobilized, which customer obligations remain covered and when can customers actually withdraw?" Those are four independent tests. Our Four-Ledger Incident Accountability Model below turns this distinction into a practical way to interpret breaking exchange-hack news without treating announcements, estimates or on-chain activity as interchangeable proof.
Key takeaways
- The incident is confirmed; its full cause is not. Mercado Bitcoin acknowledged a security event, while outside investigators documented substantial movements from addresses attributed to the platform. The initial intrusion route has not been publicly established in the sources reviewed.
- Multiple loss estimates can be reasonable at different snapshots. CoinDesk reported more than $40 million, The Block cited approximately $46.3 million, Bitquery reconstructed approximately $48.5 million and Chainalysis estimated approximately $49 million. The coverage, dates and valuation methods differ.
- The exchange's later $11.2 million blocked-asset figure is a company update. It should not be confused with Chainalysis' earlier nearly $10 million report, and the two should not be added together automatically.
- Frozen assets are not necessarily recovered assets. Issuer-level blocking may restrict transferability while legal, operational or compliance steps to return funds remain unresolved.
- A reported balance is not necessarily an available withdrawal. An exchange can recognize its obligation to customers while suspending withdrawals until controls have been validated.
- Chain coverage differs by investigator. Bitquery analyzed activity across ten chains; Chainalysis described asset movements across 17. These are scopes of individual investigations, not evidence that one dataset definitively supersedes the other.
- Customer protection remains an issuer statement. Mercado Bitcoin says clients will not bear losses and customer information was not exposed. Independent verification of every liability, key system and withdrawal route has not been supplied in the cited reports.
- A multi-chain exchange incident does not mean Bitcoin, Ethereum or Solana's base protocols were hacked. The distinction between exchange-controlled authorization and a blockchain consensus failure matters.
- A security incident is also a phishing opportunity. Beware fake refunds, WhatsApp messages, login pages, account-verification prompts and unsolicited wallet-recovery assistance.
- Self-custody changes the threat model; it does not eliminate it. Assets held under keys a user independently controls do not rely on an exchange's withdrawal queue, but users become responsible for seed backups, recipient verification and transaction approval.
What happened on November 2, 2026?
Direct summary: Mercado Bitcoin disclosed that it had identified and acted to contain a security incident in one of its systems during the early hours of November 2. It temporarily suspended customer deposits and withdrawals, said it was investigating the incident and coordinating with authorities, and published destination addresses related to the suspicious movements to assist tracing. Independent analysts described rapidly moving assets from exchange-linked wallets across numerous blockchain networks. The full method of unauthorized access, definitive scope of affected wallets and customer-service recovery timetable were not established at the reporting cutoff. InfoMoney reproduced the exchange's original and subsequent messages, while CoinDesk documented early third-party assessments.
The first statement distinguished a breach of an exchange-controlled system from customers' individual wallets: the company said its own incident response was underway, denied customer losses and denied a personal-data leak. These are statements by the exchange. The on-chain evidence concerns the movement of cryptoassets, not necessarily the downstream allocation of the economic loss between the company and its users.
That distinction matters immediately to someone with a balance on Mercado Bitcoin. The existence of unauthorized withdrawals from platform-linked addresses can coexist with a company commitment to maintain user balances. It can also coexist with a temporary inability to access those balances. Customers need confirmation of all three conditions: account balance correctness, service availability and successful settlement to independently verified destinations.
At a glance: verified reports as of November 3
| Question | Evidence-led answer | What is not established |
|---|---|---|
| When was the incident reported? | November 2, 2026 | Precise initial access and dwell time of the attacker |
| What did Mercado Bitcoin do? | Acknowledged the incident and suspended deposits and withdrawals | A verified timetable for complete restoration |
| How large was the incident? | External preliminary estimates ranged from more than $40M to about $49M | A final audited, consistently defined loss figure |
| How many networks? | Bitquery studied 10; Chainalysis described transfers across 17 | Whether their attributed-address universes and inclusion rules are identical |
| What was blocked or frozen? | Chainalysis: nearly $10M; later Mercado Bitcoin update: $11.2M | Completed return or ownership settlement of all blocked tokens |
| What about approximately $38M? | Mercado Bitcoin's later update, as reported by CNN Brasil, described about $38M still involved | A reconciled, audited explanation of this figure against earlier gross estimates |
| What did the exchange say about clients? | No customer losses or data leak, according to the company | Independent audit of every liability, data system and withdrawal route |
| Who was responsible? | No verified public perpetrator attribution in the reviewed sources | The attacker identity, original compromise mechanism and full chain of access |
| Was Binance involved? | A separate major exchange incident occurred days earlier | Any proven shared attacker or shared exploit with Mercado Bitcoin |
Timeline: why the order of updates matters
| Date / phase | Reported development | Interpretation and limit |
|---|---|---|
| Early November 2 | Suspicious transfers started from addresses researchers attributed to Mercado Bitcoin | Researcher attribution and timestamps must be distinguished from a forensic report about access credentials |
| November 2, morning Brazil time | Mercado Bitcoin said it identified and contained an incident and temporarily suspended deposits and withdrawals | The statement described its immediate response; it did not provide a complete public ledger of every address and transaction |
| November 2, initial coverage | Analysts cited $40M+ and approximately $46.3M movement estimates | Preliminary snapshots with different on-chain scopes and token valuations |
| November 2, independent tracing | Bitquery estimated $48.5M across ten chains and claimed some deposit-address outflows continued after the exchange's public containment statement | Independent findings, not a confirmed explanation of whether each post-statement transfer was attacker-initiated or an authorized recovery action |
| November 2, Chainalysis response | Chainalysis reported approximately $49M in stolen assets and nearly $10M frozen | Investigator's report includes a wider multi-chain investigation; a freeze is not a refund |
| November 2, later company update | Mercado Bitcoin said $11.2M blocked and reported around $38M still involved, according to CNN Brasil | Later company figures; not automatically additive to, or comparable with, earlier outside estimates |
| As of November 3 cutoff | Full technical report, complete funds recovery and a universal withdrawal-restoration confirmation were not established in the reviewed evidence | Users must check current official status before attempting transfers |
The most important editorial discipline is to resist converting a sequence of estimates into a fabricated single balance sheet. A defensible reconstruction requires the same measurement date, address universe, token pricing, treatment of internal transfers and definition of "blocked" or "recovered." These pieces have not all been published in a reconciled form.
How much was stolen from Mercado Bitcoin? Reconciling the numbers
The most prominent figures are not simple contradictory guesses. Each belongs to a particular reporting source and analytical purpose. The table below preserves those distinctions rather than selecting the largest number for the headline and treating everything else as wrong.
| Report or source | Reported amount | What the number describes | Main limitation |
|---|---|---|---|
| CoinDesk / early investigators, Nov. 2 | More than $40M | Initial value of suspected outflows from exchange-linked wallets | Early estimate; chain coverage and valuation may expand |
| The Block, citing Arkham, Nov. 2 | Approximately $46.3M | On-chain value attributed to the exchange incident | Third-party address labels and market prices |
| Bitquery, Nov. 2 | Approximately $48.5M | Its detailed reconstruction across 10 blockchains | Attribution, chosen cutoff and methodology are Bitquery's; not an audit of company accounts |
| Chainalysis, Nov. 2 | Approximately $49M | Assets it described as stolen across 17 blockchains | Investigative value at its own scope and time |
| Chainalysis, Nov. 2 | Nearly $10M frozen | Assets immobilized through coordinated intervention | Not a completed recovery or an amount to add to later freeze reports |
| Mercado Bitcoin, later Nov. 2 update via CNN Brasil | $11.2M blocked | Company's reported blocked assets | Different statement and potentially later snapshot from Chainalysis |
| Mercado Bitcoin, later Nov. 2 update via CNN Brasil | Approximately $38M still involved | Company's own description of assets still implicated in the incident | Precise accounting category and comparability with gross outflows need clarification |
Chainalysis' incident report and Bitquery's transaction reconstruction are independent investigations with different analytic scopes. CNN Brasil's later coverage reports the exchange's blocked-asset update. The Block supplies a separate Arkham-based valuation.
Why $49 million minus $11.2 million is not a verified outstanding loss
It is tempting to subtract $11.2 million from $49 million, obtain $37.8 million, and call that the unrecovered loss. That arithmetic is simple but its accounting interpretation is not established. The figures came from different organizations, time snapshots and potentially different address-attribution and pricing methods. Blocking can be temporary; other assets may be outside the freeze perimeter; money can move during the reporting interval; and token values can change. The roughly $38 million in the exchange's own later statement is directionally similar, but this does not prove a reconciled freeze-adjusted balance or settled customer liability.
A credible remaining-at-risk number would require a documented opening amount, clear asset-by-asset definition, identical valuation conventions, verifiable frozen balances, legally recoverable custody status and actual return or restitution events. These conditions are not met by subtracting two headlines.
Is the incident value the same as the customers' losses?
No. Exchange-controlled assets can be moved without the entire economic loss being passed to users. A company may maintain customer account balances while absorbing an impairment on its own balance sheet, replenishing reserves, using available liquidity or recovering blocked tokens. Conversely, a promise to protect balances is not itself an audit that all liabilities are backed at every moment. Bloomberg Línea reported the exchange's statement that it expected to bear the incident's losses rather than charge its customers. That is a company commitment, not proof of its final execution.
Did Mercado Bitcoin really contain the attack?
The exchange said it identified and rapidly contained a security incident. However, Bitquery's November 2 research reported that additional outflows from addresses it attributed to customer deposit infrastructure continued after the exchange's first public containment statement. Bitquery specifically cited a large set of Ethereum deposit addresses and activity extending later in the day.
This discrepancy is important, but its interpretation needs restraint. An outside investigator can observe on-chain transfers and make address attributions. It generally cannot, from a transaction record alone, determine the internal reason every transfer was signed. Some transfers might be unauthorized drains, emergency sweeps, custody reorganizations or other operations requiring further explanation. Bitquery characterized the activity as continued attacker draining; that is its reported conclusion, not an independently established root-cause finding by Terenval or a statement subsequently reconciled by the exchange in the sources reviewed.
Terenval's operational lesson: A statement that an entry point has been contained is different from proof that every vulnerable credential was rotated and every affected address stopped moving. An exchange may isolate an application, halt retail transactions, block specific tokens and still need to secure additional signing systems or reconstruct historical activity.
Why two analysts can count ten and seventeen blockchains
Bitquery described a ten-chain transaction-by-transaction investigation. Chainalysis described suspicious asset movements across seventeen chains. It would be misleading to convert the smaller number into a claim that no other networks were affected, or to present seventeen as a reconciled platform-wide count certified by both firms. Investigators may include different chains, linked addresses, token classes and successive hops, and may observe the case at different points in time.
The practical conclusion for users is more useful than the raw chain count: the attack was reported at the exchange-custody layer, with assets present on multiple networks. Securing one wallet or pausing one chain's withdrawal route may not by itself secure every asset, bridge route or signing workflow used by a multi-chain exchange.
What is a crypto exchange hot wallet, and what may have failed?
A hot wallet holds or uses spending credentials in a system connected to an online operational environment. Exchanges often use hot wallets and automated signing infrastructure to process customer deposits, withdrawals, market-maker transfers and internal treasury movements. A cold wallet aims to keep signing material or approvals separate from routine internet-facing services. These definitions describe a control architecture, not a guarantee that one group of keys can never be compromised.
Mercado Bitcoin's public disclosure did not establish a detailed exploit chain. The published on-chain analysis shows or alleges unauthorized movement from exchange-linked addresses, but does not prove whether the original access came from leaked private keys, administrator credentials, a signing-service compromise, supply-chain malware, a malicious insider, or a software vulnerability. The common feature across these hypotheses is the need for spending authority or sufficient control over a process that can exercise it. None of the hypotheses should be stated as fact without an incident post-mortem.
A compact guide to the security boundaries
| Component | What it normally controls | What a compromise could affect | What remains unknown here |
|---|---|---|---|
| Exchange login / customer database | User authentication and account records | Account access, personal data, support-channel risk | Mercado Bitcoin said no customer data leaked; no independent technical audit cited |
| Withdrawal engine / operations service | Validates and routes customer payout requests | Withdrawal authorization, limits, reconciliation | Precise failure mechanism not publicly described |
| Hot-wallet signer | Signs authorized blockchain transfers | Spendable online balances across supported networks | Which signing credentials were reached, and how |
| Cold-storage / external approval process | Isolates or separately approves certain transfers | Larger reserves if its controls fail | No verified report that all cold systems were compromised |
| Deposit-address infrastructure | Issues or tracks addresses for customer deposits | Incoming-payment accounting, movement of deposit funds | Bitquery attributed large-scale deposit-address outflows; scope not officially reconciled |
| Stablecoin issuer / freeze authority | May restrict certain tokens at the contract level | Movement of some stolen issued tokens | Freezable amounts, legal status and ultimate return of blocked funds |
A single public blockchain address does not reveal the deployment topology of the institution that controls it. One organization may operate multiple signers and wallets across chains; one key or workflow might also have authority over many individual addresses. The public investigation cannot be used to infer a specific seed-phrase leak or to tell customers that their personal wallet recovery words were exposed.
What does 'funds frozen' actually mean?
A freeze usually means an asset or address has been made unable to transfer specified tokens through an issuer- or platform-controlled mechanism. Some centrally issued stablecoins contain smart-contract functionality that permits authorized freezing or blacklisting under issuer policy and relevant legal processes. By contrast, the public Ethereum network does not provide a universal administrator who can freeze all ordinary ETH balances, and Bitcoin transactions cannot be reversed by a central token issuer.
In its November 2 response, Chainalysis said it coordinated with law enforcement and organizations including Tether, Circle, Paxos, Anchorage Digital and Ripple. The firm described tracing freezable assets and said action by Tether had frozen over $9 million of stolen funds associated with the incident. Mercado Bitcoin's later update reported a broader blocked-asset total of $11.2 million through coordinated work with issuers and investigative partners. These statements provide evidence of intervention; they are not a public settlement receipt establishing where the funds will ultimately be delivered.
Four stages of crypto-asset recovery
| Stage | What has happened | What it proves | What it does not prove |
|---|---|---|---|
| 1. Traced | Analysts identify transaction paths and probable linked wallets | A specific value and destination may be visible on-chain | The investigator has control of the tokens |
| 2. Frozen / blocked | A competent actor restricts movement of a relevant token or account | Part of the stolen value may be temporarily immobilized | Tokens have been legally reassigned or refunded |
| 3. Returned / recovered | Assets are transferred back to authorized control after appropriate processes | The owner or responsible institution regains control | All remaining liabilities or losses are resolved |
| 4. Customer access restored | A user can verify and complete a safe withdrawal | A functioning settlement route exists for that user, asset and chain | Every platform balance or network is necessarily available |
This four-stage description is a Terenval explanatory framework, not an official Mercado Bitcoin accounting statement or legal determination. It is useful precisely because a headline such as "millions recovered" may be using "recovered" informally for tokens that were only frozen at the reporting cutoff.
Why can USDT be frozen while stolen BTC remains mobile?
USDT is a centrally issued token with contractual controls that may allow the issuer to freeze balances under defined circumstances. A Bitcoin UTXO is not governed by Tether's token contract; moving or immobilizing it follows different rules. Centralized exchanges may refuse stolen deposits and authorities may intervene at other points, but that differs from freezing an ordinary Bitcoin output by administrative command. Likewise, not every token on Ethereum has a freeze function; issuer contracts and legal policies vary. No user should assume that an asset is recoverable merely because investigators can trace it.
Terenval original analysis: the Four-Ledger Incident Accountability Model
Original editorial model: A centralized-exchange security event should be evaluated using four ledgers that answer different questions. The Four-Ledger Incident Accountability Model is a framework designed for readers, analysts and treasury operators to avoid confusing blockchain activity with customer welfare. It is not a formal financial audit, insurance assessment or measurement of Mercado Bitcoin's solvency.
| Ledger | Core question | What evidence helps | Why this ledger is distinct |
|---|---|---|---|
| Ledger A — On-chain movement | Which cryptoassets left which controlled addresses, and when? | Transaction hashes, chain IDs, token contracts, attribution sources, time-specific USD prices | Establishes movements, not who ultimately bears the loss |
| Ledger B — Intervention and recovery | Which assets are traced, blocked, returned or irretrievable? | Issuer freeze notices, law-enforcement coordination, verified return transactions | Blocking and returning are different states |
| Ledger C — Customer obligations and backing | Does the company still recognize and have resources to honor client balances? | Customer ledger, reserve reconciliation, audited statements, replenishment plan | An on-chain theft need not equal a customer's recorded balance loss |
| Ledger D — Operational access | Can a customer safely withdraw or deposit the claimed asset today? | Live network-specific withdrawal status, transaction completion, deposit-address validation | A claim on assets is not the same as immediate settlement ability |
The central insight: An exchange could score poorly on Ledger A while protecting Ledger C by absorbing a theft. It might improve Ledger B through stablecoin freezes while Ledger D still shows suspended withdrawals. Conversely, reopening a single withdrawal route in Ledger D is not proof that all affected tokens in Ledger B were returned or that Ledger C has been independently audited.
The model also suggests four more transparent incident-update questions for exchanges: (1) Which assets and chains remain affected? (2) Of each chain's attributed value, how much is only traced, frozen, actually returned or still moving? (3) What precisely supports the claim that customer balances are fully covered? (4) Which deposit and withdrawal routes have actually been tested and reopened? Reports that answer all four are materially more useful than a single headline percentage.
A hypothetical example: why a 'fully protected' account can still be inaccessible
Consider a fictional customer with $5,000 equivalent in a custodial exchange account. Suppose the exchange recognizes the full $5,000 balance and promises to absorb a separate corporate wallet loss, but all withdrawals remain paused for 48 hours. The customer's recorded claim remains $5,000 while their immediate ability to transfer that claim on-chain is restricted. No arithmetic should transform the paused balance into a realized $5,000 loss; at the same time, it is inaccurate to say the customer already has unrestricted control of their funds.
This is not a report about any specific Mercado Bitcoin account. It illustrates why user-facing reliability should be measured by both balance coverage and verifiable settlement, rather than one assurance replacing the other.
The Cross-Chain Containment Gap: an additional operational test
A second original Terenval concept, the Cross-Chain Containment Gap, measures the difference between an institution's first declaration of containment and its independently corroborated last unauthorized transaction within the affected perimeter. Ideally, this interval is zero or negative; if investigators credibly document later unauthorized movements, the response perimeter may have been incomplete or the announcement may have described only one isolated system.
This is a diagnostic question, not a calculation of the Mercado Bitcoin breach duration. Determining the gap requires proof that each later transfer was unauthorized, accurate timestamps, chain finality, verified address ownership and a clear definition of what the company meant by "contained." Bitquery reported relevant later movements, but the public record reviewed here is insufficient for Terenval to assign a certified gap in minutes or hours.
What crypto users should know
The recommendations below are general defensive precautions. They are not claims that Mercado Bitcoin has instructed every client to move funds, change a specific account setting or use a particular withdrawal route. If a platform is responding to an active incident, authenticated, current guidance from that platform should take precedence over any static news article.
1. Verify the current official status of deposits and withdrawals
Open the official Mercado Bitcoin app or website through a known bookmark or address you type yourself. Confirm whether your specific asset and network supports deposits and withdrawals, because an exchange can restore services in stages. The source reports reviewed here did not establish a universal, time-specific all-clear for every route as of November 3. Do not infer availability from a successful login, a social-media repost or another exchange's status page.
2. Do not reuse a saved deposit address without reconfirming it
If you were planning to deposit BTC, ETH, USDT, USDC or another token, obtain a freshly verified address and network from the authenticated exchange interface after the service is confirmed available. Saved addresses may be unavailable, disabled, replaced or tied to an unsupported temporary route. Sending funds to a formerly valid address during an incident can complicate accounting or leave a transfer uncredited. Terenval's guide on choosing the correct network for an exchange withdrawal explains why network and address checks are separate.
3. Keep a safe record of your account and pending transactions
Preserve the visible asset and amount, network, order or withdrawal reference, transaction hash if one exists, and UTC timestamps. Do not publish account IDs, identity documents, phone verification codes or private recovery words in public comments. If a withdrawal request was submitted before the pause, check whether it was broadcast, queued, cancelled or settled; those statuses are not interchangeable.
4. Treat all 'recovery assistance' as a phishing risk
The exchange specifically warned against fake support and refund approaches, according to CNN Brasil's account of its later statement. Mercado Bitcoin said it does not ask users for passwords, verification codes or recovery phrases and does not provide reimbursement through unsolicited links, WhatsApp messages or phone calls. If someone asks for those items, do not comply. Refer to Terenval's phishing glossary for the difference between authentic account support and credential theft.
5. Separate your exchange account risk from your independent wallet risk
A custodial exchange incident does not by itself establish that the private keys of a separate self-custody wallet have been exposed. Likewise, receiving a suspicious token does not prove the seed is stolen. Only rotate keys, revoke approvals or migrate assets when the relevant evidence supports that response. If you independently suspect compromise of your own signing credentials, follow a separate, controlled plan such as Terenval's guide to moving crypto after a security compromise.
6. Confirm full addresses rather than copying history entries
Breaking incident news often attracts address-poisoning campaigns and fraudulent support deposit requests. A shortened familiar address is not evidence of a trusted recipient. Use a fresh authenticated deposit address, compare the entire destination, and verify the exact asset and network before a high-value transfer. Terenval's detailed crypto address-poisoning guide describes how attackers seed similar-looking addresses into transaction histories.
7. Do not treat a test transfer as permission to resume normal operations
A small successful test shows that a particular route worked for that transaction; it does not prove the exchange has reopened every network or that its internal security review is complete. Test transfers are appropriate only after the recipient has been independently verified and the platform has confirmed the relevant route can be used. A small amount sent to a malicious or stale address can still be lost.
A practical decision matrix for users and businesses
| Your situation | What to verify first | Risk to avoid | Conservative action |
|---|---|---|---|
| Customer with a displayed Mercado Bitcoin balance | Whether the account ledger is accurate and withdrawals are currently enabled for your asset | Assuming a visible balance means settlement is available | Keep records; consult official announcements and per-network withdrawal status |
| Customer with a pending withdrawal | Request ID, broadcast status, TXID, network and destination | Paying third parties to 'unfreeze' an ordinary queue | Use in-app support and authenticated transaction details |
| Customer preparing a new deposit | Current deposit support, fresh address, token and chain | Sending to a stale address or wrong network during the pause | Wait for confirmed reopening and independently verify the full destination |
| User holding crypto in an unrelated self-custody wallet | Your own transaction history, app integrity and approvals if there is a separate reason for concern | Panic-importing seed phrases because a custodial exchange was breached | Keep secrets offline and react to evidence specific to your wallet |
| Business with automated exchange settlements | API status, account controls, deposit addresses, queues and payout rules | Automatically restarting jobs when a news headline says 'contained' | Pause affected flows; restart only after official status and independent route validation |
| High-value holder comparing custody models | Key ownership, backup quality, ability to transact, operational burden | Assuming all exchange funds or all self-custody funds are equally safe | Consider diversification and a documented recovery plan; evaluate trade-offs, not slogans |
Why it matters: security, liquidity and custody are different promises
Mercado Bitcoin is a major participant in Brazil's cryptocurrency market. A deposit-and-withdrawal suspension affects people who depend on a centralized platform to move assets, whether or not the platform ultimately absorbs the direct theft. A temporary pause can prevent an attacker from triggering more user-facing activity, but it can also interrupt ordinary savings transfers, merchant payments, portfolio rebalancing and planned liquidity needs.
An exchange has at least three relevant responsibilities during a security event: prevent further unauthorized spending, maintain accurate customer liabilities and safely restore operational access. These objectives can conflict in the short term. Keeping withdrawals paused may reduce immediate exposure while limiting customer access. Reopening too early may restore convenience while increasing risk if compromised signers or internal controls remain trusted.
For market participants, the incident is also a warning about shared custody infrastructure. A platform supporting BTC, Ethereum and many other chains must secure a complex collection of signers, token contracts, address-generating services, deposit monitors, bridges or routing tools and operational permissions. A visible movement across many networks is not proof that every blockchain protocol was broken; it may instead reflect the breadth of access held by the exchange's own custody and treasury workflows.
What the event says about proof of reserves
A reserves page, snapshot or a list of proof-of-reserves wallet addresses can help demonstrate on-chain holdings at a particular time. It does not, by itself, guarantee that funds will remain protected after the snapshot, prove the absence of hidden liabilities, provide a complete financial audit or ensure immediate liquidity on every chain. A security incident therefore raises additional questions: Which reserves were exposed? How were customer liabilities reconciled after the outflows? Which funds are replaceable by the company's own resources? Has an independent reviewer attested to the resulting position? The articles reviewed for this report do not provide a sufficient basis for a definitive answer on Mercado Bitcoin's entire post-incident balance sheet.
Self-custody versus exchange custody: the useful distinction
In a custodial exchange account, the platform generally controls the spending infrastructure and maintains an internal accounting claim for the user. A customer may depend on the provider's service availability, financial condition and security response to withdraw. In an independently controlled non-custodial wallet, the user or designated signing arrangement holds the relevant private-key authority and can authorize transfers subject to network availability and wallet compatibility.
That difference creates a real option for people who wish to reduce reliance on a single exchange's withdrawal service. It does not prove that self-custody is effortless or immune to theft: phishing, exposed recovery phrases, incorrect networks, malicious approvals and destination-address mistakes can still cause permanent losses. Terenval's non-custodial wallet glossary and seed phrase vs. private key guide explain the responsibilities that come with controlling signing credentials yourself.
Where Terenval Wallet fits
Terenval Wallet is a self-custody wallet within the Terenval ecosystem. For readers considering independent custody, the relevant question is not whether a wallet brand claims that exchange failures can never affect you; it is whether the wallet's documented asset support, networks, recovery method and signing model fit your actual needs. A properly controlled wallet can remove dependence on one centralized exchange's withdrawal queue for funds already held under your independent keys. However, importing an already compromised recovery phrase into Terenval—or any other wallet—does not make that secret safe. Verify the product's current supported capabilities and backup procedures before moving assets. This is contextual product information, not a claim that Terenval was involved in the incident or has an automated protection feature against Mercado Bitcoin's unidentified attack.
The editorial conclusion is deliberately non-promotional: choose custody based on the security work you can perform reliably, not the assumption that a particular interface is a substitute for sound key management.
Impact on Bitcoin, Ethereum, Layer 2, DeFi and wallets
Bitcoin: unauthorized transfers do not establish a protocol break
Bitcoin was among the networks cited in on-chain investigations. That is not evidence of a Bitcoin consensus-layer exploit, a failure of signatures or a defect in the network's transaction finality. An authorized signing key used by an attacker can create a blockchain-valid transfer even when it violates the exchange's business rules. Once confirmed, that transaction is not ordinarily reversible by asking the Bitcoin network to undo it.
Ethereum and stablecoins: tracing plus targeted intervention
Ethereum transfers offer visible transaction records and event logs that can help investigators follow movements. Stablecoins issued through contracts with administrator or compliance controls may be subject to issuer-initiated freezes. The Chainalysis report describes how rapid intelligence sharing helped Tether and other partners target stolen assets. That should not be confused with a universal ability to reverse all ERC-20 transfers, freeze native ETH or obtain restitution automatically.
Layer 2: a wider custody perimeter, not necessarily an L2 failure
Arbitrum, Base and other Ethereum-related networks appeared in the described multi-chain activity. A centralized platform may operate spending infrastructure separately or jointly across multiple EVM-compatible environments. The critical risk is how those transaction rights are managed and monitored. The incident reports do not establish a consensus flaw in Arbitrum or Base merely because an exchange-linked wallet made an unauthorized transfer there.
Solana, Tron and other networks: network-specific responses
Cross-chain investigations require chain-specific transaction identifiers, asset metadata and custody controls. The difference between an exchange's blocked withdrawal route, an issuer's token freeze and an on-chain transaction broadcast is especially important across heterogeneous networks. Investors should verify the precise chain and token contract rather than assuming that a symbol such as USDT always represents one identical asset or recovery mechanism.
DeFi: do not invent a smart-contract exploit
A stolen asset may later pass through a decentralized exchange or bridge, making tracking and intervention more complicated. However, the fact that such services appear in a money trail does not prove a vulnerability in the protocols themselves. The sources reviewed for this report do not establish a particular DeFi exploit as the root cause of Mercado Bitcoin's breach.
Other exchange incidents: similarity is not attribution
The Mercado Bitcoin incident followed a separately reported major Binance compromise by several days. Their temporal proximity and status as centralized platforms do not establish that the same attacker, malware, credential route or technical vulnerability was responsible. The incidents must be investigated independently. For context on a distinct exchange's reserve-replenishment and withdrawal-restart process, see Terenval News' Binance recovery report. Its figures should not be added to or used to validate the Mercado Bitcoin estimates.
Frequently asked questions
Was Mercado Bitcoin hacked on November 2, 2026?
Mercado Bitcoin publicly confirmed a security incident on November 2 and suspended deposits and withdrawals. Blockchain investigation firms described unauthorized cryptocurrency movements from addresses attributed to the exchange. The public reporting reviewed here does not establish the precise initial intrusion path.
How much cryptocurrency was stolen from Mercado Bitcoin?
Chainalysis estimated about $49 million, while other contemporaneous third-party investigations reported more than $40 million, around $46.3 million or about $48.5 million. These values are preliminary and may use different chain coverage, token prices and timestamp conventions. They are not an independently audited final company loss.
Did Mercado Bitcoin freeze $11.2 million in stolen assets?
The exchange said it blocked $11.2 million, according to its later November 2 statement reported by CNN Brasil. This company-reported figure is later than Chainalysis' description of nearly $10 million frozen. It does not prove that the money has already been returned.
Why did Chainalysis report nearly $10 million frozen instead of $11.2 million?
The statements represent different reporting entities and time-specific updates. Some additional assets may have been blocked later, but the public evidence cited here does not supply a fully reconciled asset-by-asset explanation. Do not add the two numbers or treat the difference as a confirmed new recovery tranche.
Does $38 million represent the unrecovered balance?
Not as a verified, audited figure. CNN Brasil reported Mercado Bitcoin's reference to about $38 million still involved in the incident. Its relationship to earlier investigator valuations has not been published in a complete reconciliation. It should not be declared the exact net customer loss.
Did Mercado Bitcoin customers lose money?
The exchange says customers suffered no losses and that it would protect their assets. This is a company assertion. Whether each customer can immediately use or withdraw the corresponding funds is a separate operational question, and a complete independent balance-sheet assessment was not available in the cited material.
Was Mercado Bitcoin customer data leaked?
Mercado Bitcoin said no customer data leaked. No independent forensic account reviewed here establishes the complete access scope. Customers should still watch for impersonation scams and protect their authentication credentials.
Are Mercado Bitcoin deposits and withdrawals working again?
Deposits and withdrawals were suspended following the November 2 incident. The sources reviewed for this article did not verify a universal resumption of every asset and network by the November 3 cutoff. Check the current authenticated platform status for your specific route before sending funds.
How many blockchains were affected—ten or seventeen?
Bitquery reconstructed transactions on ten blockchains; Chainalysis described movements across seventeen. Different investigative scope and attribution can explain the difference. Neither report is a public certification of the company's complete chain-by-chain inventory.
Can a stablecoin issuer reverse a stolen transfer?
Some issuers can freeze certain contract tokens, restricting their subsequent movement; that is different from reversing the blockchain transaction or returning the tokens. The legal and operational steps necessary to restore ownership can continue after an asset is frozen.
Does a freeze mean the hacker no longer controls any cryptocurrency?
No. Only assets covered by effective freeze or blocking actions are restricted. Other assets, including ordinary BTC or ETH, may remain movable if the attacker retains the relevant signing authority. Monitoring and recovery can continue after the first successful freeze.
Does the incident mean Bitcoin or Ethereum was hacked?
There is no evidence in the reviewed reports of a Bitcoin or Ethereum consensus failure. The reported risk concerns exchange-linked assets and custody infrastructure, not a demonstrated break of either blockchain's underlying validation rules.
Should I enter my Mercado Bitcoin seed phrase into a recovery website?
No. An exchange-account support process should not require a private wallet recovery phrase. Mercado Bitcoin specifically warned about fake reimbursements and requests for passwords, verification codes and recovery phrases. Use only independently verified official channels.
Is it safer to move everything to a self-custody wallet immediately?
Not automatically. A self-custody wallet changes who controls signing credentials and reduces dependence on an exchange withdrawal service once assets are under the user's independent keys. It also introduces backup, phishing, device and transfer-error risks. Do not attempt a withdrawal if the exchange has suspended it or instructs users to wait; verify routes and addresses before any future transfer.
Did the attacker steal private keys from Mercado Bitcoin?
The precise intrusion and signing mechanism has not been established in the cited evidence. Unauthorized signed transactions and researcher observations do not by themselves prove a particular stolen seed, password, API key or server exploit. A technical incident report would be needed to make that attribution.
Are the Mercado Bitcoin and Binance incidents linked?
No verified link between perpetrators or exploit mechanisms was established in the reports reviewed for this article. The incidents occurred close together but should not be combined into a single attack narrative without supporting investigation evidence.
What remains unknown and what to monitor next
The incident's root cause, exact set of compromised signing systems, complete address attribution, final total affected value, reconciliation between the different frozen-asset figures, the legal status of blocked tokens, independent verification of customer balance coverage and a timetable for restoring every service remain material open questions at this article's cutoff.
The most useful follow-up disclosures would be: an authenticated exchange incident review with a chronology; an asset-by-asset reconciliation across all affected networks; evidence of what was frozen versus actually returned; a documented plan for replenishing any company funds; independent assurance about the customer ledger; and route-specific confirmation that deposits and withdrawals are safely operational. Each is a separate milestone.
For customers, the next action does not depend on predicting which headline estimate ultimately proves closest to the audited amount. It depends on authenticated status information for their asset, the preservation of transaction records, the protection of credentials and their ability to verify a safe destination whenever the platform authorizes transfers again.
Related content suggestions
If the distinction between company-controlled reserves and your own recovery secrets is unclear, read Terenval's Seed Phrase vs Private Key vs Wallet Password and the non-custodial wallet glossary. For secure recipient selection when withdrawals reopen, see What Is Crypto Address Poisoning? and How to Choose the Correct Network When Withdrawing Crypto.
For a separate security incident involving merchant-controlled signing systems rather than a custodial exchange, see BTCPay Server Hot-Wallet Drains: What Merchants Should Do. Another distinct key-management issue was covered in Qubic's weak-seed wallet report. Comparing these reports helps identify the correct threat model without implying that they share a perpetrator or exploit.
Sources
- Chainalysis — Disrupting the Mercado Bitcoin Attack, November 2, 2026 — First-hand investigative response; approximately $49 million described as stolen across 17 blockchains; coordinated freeze actions and nearly $10 million immobilized at its reporting cutoff.
- CNN Brasil — Mercado Bitcoin Reports $11.2 Million Blocked, November 2, 2026 — Later company statement about blocked assets, assets still implicated, partners and warnings about fake reimbursements.
- CoinDesk — Mercado Bitcoin Halts Withdrawals After More Than $40 Million Drained, November 2, 2026 — Early investigation and exchange disclosure, including operational suspension.
- The Block — Mercado Bitcoin Breach Estimated at $46.3 Million, November 2, 2026 — Arkham-based valuation and reporting on initial freeze actions.
- Bitquery — Mercado Bitcoin On-Chain Investigation, November 2, 2026 — Detailed ten-chain reconstruction, deposit-address attribution and reported post-announcement movement; independent analysis requiring contextual interpretation.
- InfoMoney — Mercado Bitcoin Incident Messages, November 2, 2026 — Portuguese-language reproduction of the original incident announcement and subsequent monitoring update.
- CNN Brasil — Initial Incident Disclosure, November 2, 2026 — Exchange position on customer impact, data exposure and the initial operational pause.
- Bloomberg Línea — Company Commitment to Bear the Losses, November 2, 2026 — Report of the exchange's intent to absorb incident costs rather than charge customers.
- Portal do Bitcoin — Exchange's Official Statement Reproduced, November 2, 2026 — Independent reproduction of Mercado Bitcoin's first announcement and customer-protection claims.
- Folha / C-Level — Mercado Bitcoin Recovery Update, November 3, 2026 — Follow-up account of the company-reported blocked amount and outstanding exposure.
Editorial context
Information cutoff: November 3, 2026. This article is based on public statements by Mercado Bitcoin as reproduced by Brazilian news organizations, first-hand investigative reporting by Chainalysis, and separate on-chain valuations and reconstructions by CoinDesk, The Block and Bitquery. Where researchers differ in the number of chains or the amount moved, their claims are attributed rather than silently merged. The exchange's claims of no customer losses and no data leak are reported as its assertions, not presented as independently certified facts. Assets traced, assets blocked and assets actually returned are different accounting conditions; this report makes no unsupported claim that the full theft has been recovered or that all withdrawal routes have reopened. Bitquery's description of later deposit-address movements is an attributed outside finding, not a Terenval forensic attribution of specific signing activity. The Four-Ledger Incident Accountability Model and Cross-Chain Containment Gap are original explanatory tools for interpreting security disclosures; they are not formal audits, official Mercado Bitcoin remediation instructions or investment advice. Terenval Wallet is mentioned only as a contextual example of independent self-custody, without unsupported claims about its capabilities or involvement in the incident. Readers should prioritize current authenticated platform instructions and professional security guidance when an active incident affects their account.